
When Minutes Matter: Using FBI Winter SHIELD to Defend Your Business in an AI-Driven Threat Environment
 Listen to this article
The cybersecurity clock starts when a weakness becomes visible to an attacker, not when the company realizes it has been breached. AI has shortened that clock from weeks to minutes, by helping attackers find vulnerabilities, craft convincing scams, and exploit gaps at lightning speed. That is why minutes matter: the faster a company can prevent, detect, contain, and recover, the less likely a single weakness becomes a material event.
That is not hyperbole. It is the operational reality in today’s AI-accelerated threat landscape. Any one of these can start the clock: a single phishing click, a misconfigured cloud account, an unpatched firewall, or a contractor with too much access. These can be easily discovered, weaponized, and exploited before anyone notices something is wrong.
Attackers are using AI to scan the internet for vulnerable systems around the clock, generate flawless phishing emails in any language or executive voice, automate reconnaissance across entire industries overnight, and chain exploits together at machine speed. The window between exposure and compromise is collapsing. The window between compromise and serious business damage is collapsing with it.
This is the new reality for every organization, regardless of size. In fact, smaller firms are increasingly attractive targets precisely because attackers assume they have leaner IT teams, no dedicated security leader, and fewer layers of defense. The good news is you do not need a Fortune 500 budget to be meaningfully harder to compromise. You need discipline around fundamental cyber practices.
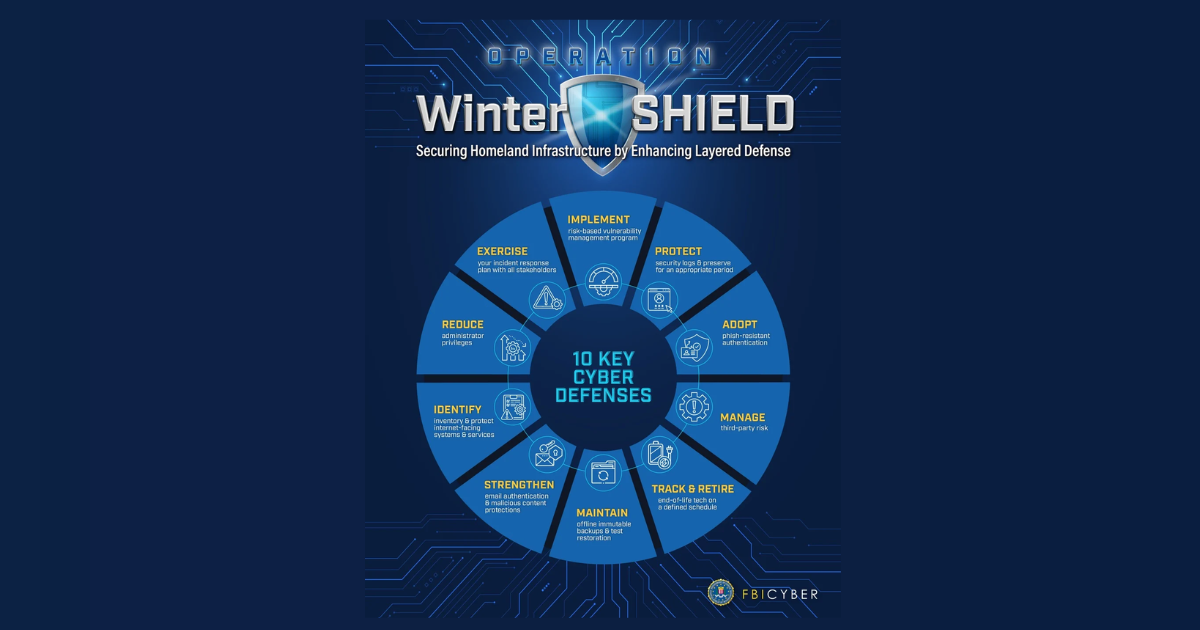
That is exactly what the FBI's Operation Winter SHIELD provides, a framework distilled from real-world investigations into how organizations actually get breached. It is not a new technology stack. It is a return to fundamentals, sharpened for an era in which fundamentals are the only things fast enough to matter. Six overarching themes summarize Winter Shield’s framework.
Know what you have, and what's exposed. You cannot defend what you have not inventoried. Every organization needs a current, accurate picture of every internet-facing system, application, cloud service, remote access tool, and vendor connection. AI-driven scanners will find the forgotten server, the test environment someone spun up two years ago, or the open port on a branch office firewall before your team does. Risk-based vulnerability management ensures the things that matter most get fixed first, with named owners and clear deadlines. Unknown exposure is the single easiest way for an attacker to get in.
Retire what's expired. End-of-life software, hardware, and operating systems accumulate unpatched vulnerabilities the moment vendor support ends. The Windows server still running because "it works fine," the network appliance the vendor stopped updating, and the line-of-business application no one wants to migrate. Each of these is an invitation for bad actors. Track end-of-support dates, retire on a schedule, and require formal risk acceptance with compensating controls for any exception.
Shrink the blast radius of every account. Excessive administrator privilege is what turns a single compromise into a company-wide event. When an attacker lands on a privileged account, they move sideways across systems, disable defenses, steal data, and deploy ransomware in hours. Administrator access must be separated from everyday user accounts, granted only when needed, reviewed regularly, and monitored. That is why phish-resistant multi-factor authentication like hardware keys, biometrics, and passkeys is non-negotiable for executives, IT administrators, remote access, financial systems, and email. The goal is to make stolen credentials useless.
Harden the front door: email. Email is still the single most successful entry point for phishing, Business Email Compromise (BEC), vendor fraud, and executive impersonation. AI has made these attacks nearly indistinguishable from legitimate messages, perfect grammar, accurate context, plausible tone, and the right names in the right places. Proper DMARC, DKIM, and SPF configuration, advanced filtering, impersonation detection, and easy employee reporting are table stakes. Assume your people will be targeted by content that looks exactly like the real thing, because they will be.
Manage the people and partners who can hurt you. Vendors, contractors, service providers, and software platforms frequently hold the keys to your systems and sensitive data. Supply chain exposure is one of the fastest-growing attack vectors. Attackers know this and increasingly come in through the weaker third party. A cyber review before contract execution, security and AI requirements written into agreements, mandatory incident notification obligations, and periodic reassessments must become the norm, not a checkbox at procurement.
Prepare to detect, respond, and recover. When something does happen, three capabilities determine whether the event becomes a footnote or an existential problem. First, protected security logs which are centralized, tamper-resistant, and retained long enough to investigate. Attackers routinely delete logs to hide their tracks; if yours can be erased, you will not know what happened or what was taken. Second, offline or immutable backups, tested with realistic restoration drills. Backups that ransomware can encrypt are not backups. Third, an incident response tabletop exercise that includes both the people who will run it and those on the front lines. The first time your CEO meets your Crisis Management or Incident Response Team cannot be in the middle of the night on the worst day of the year.
The honest measure. Winter SHIELD is not a compliance exercise. It is a leadership accountability tool, and it draws a clear line between organizations that take cyber seriously and ones that hope for the best. "Are we secure?" is the wrong question. It lets leadership off the hook with a confident-sounding answer that means nothing. The right question is harder: "Can we prove these fundamentals are in place, owned, tested, and getting stronger every quarter?" If the answer requires a pause, you already know what you must do today.
Attackers are not waiting. They are scanning your perimeter right now, drafting the email that will fool your CFO, and probing vendor connections no one has reviewed in two years. The question is not whether your organization will be tested. It is whether the fundamentals will be in place when it is. Winter SHIELD is the checklist. The countdown clock is ticking.
More info about Winter SHIELD at: https://www.fbi.gov/investigate/cyber/wintershield.
Learn more about the cybersecurity, AI, and technology strategies shaping the future of real estate at Realcomm IBcon, June 2 to 4 in San Diego. Register today!
|
Sandy Jacolow, CTO, Empire State Realty Trust
Sandy Jacolow is the SVP, CTO at Empire State Realty Trust. He oversees technology innovation supporting Financial Control, Leasing, Property Management, ESG, Marketing, and PropTech activities. He also runs ESRT’s IT and OT Cybersecurity programs working closely with the Information Technology and Compliance teams to monitor and mitigate risk associated with today’s cyber threats. He also serves as Lead for the New York InfraGard Real Estate Working Group and is a member of the RECC (Real Estate Cyber Consortium) Executive Council. |
This Week’s Sponsor
Yardi® develops and supports industry-leading investment and property management software for all types and sizes of real estate companies. Established in 1984, Yardi is based in Santa Barbara, Calif., and serves clients worldwide. For more information on how Yardi is Energized for Tomorrow, visit yardi.com.
Read Next
 9/30/2026
The Truth Is in the PDF AI has transformed what we can do with data. So why do we all still live in a sea of PDFs?
 9/23/2026
How to Put a Better Building Experience in Your Tenants’ Hands Many commercial buildings have spent the last five years adding tenant experience solutions but most of them have the same problem: the apps run on their own data.
 9/16/2026
From CIO to Orchestrator in Chief: How today’s real estate tech leaders are making change make sense Today’s CIOs operate amid sustained complexity. Portfolios are more distributed, data is more interdependent, and expectations from executives, investors, operators, and residents continue to rise.
 9/2/2026
Are We Far Behind in Our Smart Building Strategy? There is a question every building owner, facility executive, engineer, system integrator, and technology provider should be asking: Are we far behind?